Consumer Technology
Metabase Zero-Day Exploited in Wild Allows Admin Access Without Authentication - The Hacker News

What the report says
Metabase says a CVSS 10.0 zero-day SQL injection was exploited in the wild; the flaw can grant admin access and expose connected database data.
Loading debate for this article…
Other publishers covering this story
No additional verified coverage is currently clustered with this report.
Related reporting
 MUMSA Daawa Show Calls on Parents to Reclaim Role in Child Upbringing Amid Digital DistractionsNile Post
 Free internet access excites traders in Oyam marketThe Observer
 The 10 Best Home Office Gadgets To Keep You Productive - bgr.comBGR
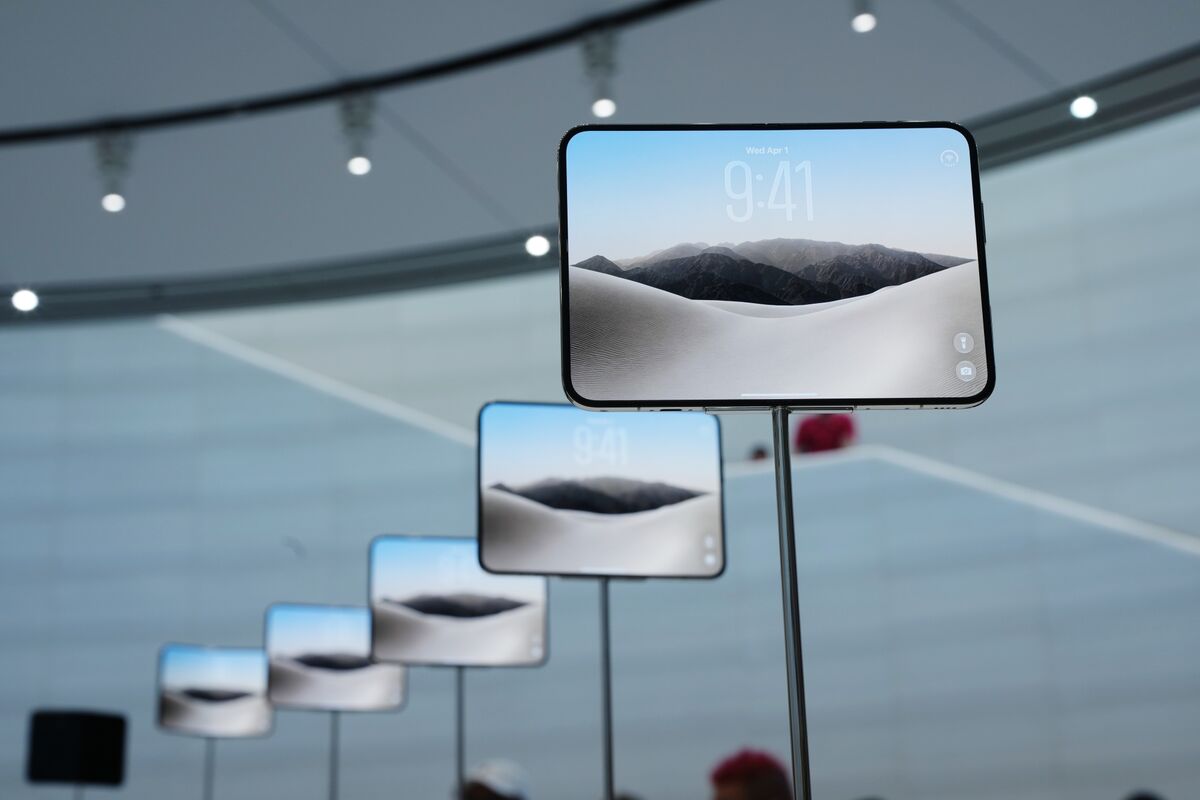 Apple’s iPhone Duo Will Turn Foldable Phones Into the New Normal - Bloomberg.comBloomberg
 Hard Times Come To An End For 3 Zodiac Signs When The Sun Aligns With Mars On Monday, September 14 - YourTangoYourTango
 Apple's iPhone Duo event should put the bears to rest - finance.yahoo.comYahoo Entertainment